Open-source SpringBoot enterprise-level technical middle platform micro-service architecture and service capability development platform

1. Project Overview
Simple and elegant · Stable and efficient | Quiet and far-reaching · Pursuing perfection
Based on Spring Authorization Server, a new adaptation of the OAuth 2.1 protocol for enterprise-level microservices architecture
Enterprise-level technical middleware microservices architecture and service capability development platform
Dante Cloud (Butterfly, originally Eurynome Cloud) is an enterprise-level microservices architecture and service capability development platform. Developed based on Spring Boot 2.7.3, Spring Cloud 2021.0.3, Spring Cloud Alibaba 2021.0.1.0, Spring Authorization Server 0.3.1, Nacos 2.1.1, etc. latest versions, following the SpringBoot programming ideology, highly modularized and configurable. Equipped with service discovery, configuration, circuit breaking, rate limiting, degradation, monitoring, multi-level caching, distributed transactions, workflow, etc. functions, code is concise, architecture is clear, and is very suitable for learning and enterprise use as a basic framework.
2. Open Source License
Licensed under Apache-2.0
3. Screenshots


4. Feature Overview
Platform Positioning
- Builds a mature, complete, and comprehensive, OAuth2-based, front-end and back-end separated microservices architecture solution.
- Designed and developed for enterprise-level applications and internet applications, both meeting the needs of traditional project microservices and satisfying the development and construction requirements of internet applications, rapid iteration, etc.
- The platform architecture uses various new and mainstream technologies in the microservices field and its surrounding areas to build, which is a tool to help quickly cross the architecture technology selection and research exploration stage.
- Code is concise and standardized, structure is reasonable and clear, and is a typical and comprehensive case for new technology development and application, helping developers to learn and master new technologies.
New version front-end features:
- Not using any popular open-source templates, using a brand-new technology stack, and completely writing a brand-new front-end project.
- Borrowing and referencing the use and design of popular open-source versions, the new version of the front-end interface style and operation habits try to unify with the current popular way.
- Fully utilizing the features of the Typescript language, solving a large number of type checking problems, and trying to avoid the use of "any" style in Typescript programming language.
- Fully using Composition Api and Hooks, etc. New features of Vue3 framework for code writing.
- Fully utilizing Component, Hooks, and Typescript object-oriented features, extracting common components and code, and trying to reduce engineering repeated code.
- Wrapping a large number of Quasar basic components and application function components for easy unified modification, maintenance, and development use.
- Deeply optimizing the performance of packaging in production mode for projects based on Vite3.
- Provide containerization packaging and deployment of engineering production code in a Docker-compose manner.
New backend features
- Based Spring Authorization Server Deep customization:
- Based Spring Data JPA, Rebuild Spring Authorization Server Basic data storage code, replacing the original JDBC data access method, breaking Spring Authorization Server Existing data storage limitations, extended to a more practical application method and design.
- Based Spring Authorization Server, On the basis of OAuth 2.1 specification, add custom 'password' authentication mode to be compatible with existing OAuth 2 specification-based, front-end and back-end separated applications.
- Based Spring Authorization ServerBased on the OAuth 2.1 specification, it adds a custom Social Credentials authentication mode, supports SMS verification codes, WeChat mini-programs, and third-party application logins.
- Follows the code standards of Spring Security 5 and Spring Authorization Serverand develops the core code of the OAuth2 authentication server, following the use of Jackson deserialization, and adds a large number of custom Jackson modules.
- Supports Spring Authorization ServerIn addition to the standard token encryption verification method of
- also added support for custom certificates token encryption methods, which can be dynamically modified through configuration.
- Supports OAuth2 OIDC authentication mode, supplements the related configuration operations of OIDC authentication in the front-end, and supports the /userinfo interface call and client registration.
- Supports OAuth2 Authorization Code PKCE authentication mode.Spring Authorization ServerExtends Client Credentialsdefault
- Supports OAuth2 Authorization Code PKCE authentication mode.Spring Authorization ServerExtends Client Credentialsmode to implement the creation of Refresh Tokens.
- mode to implement true Scope permission validation. Adds client Scope permission configuration function and decouples it from the existing user permission system.Spring Authorization ServerCustomizes
- authorization code mode login authentication page and authorization confirmation page, authorization code mode login uses data encryption transmission. Supports multiple types of verification codes, does not support behavior verification codes.
- Large-scale adjustment and optimization of code structure:
- Strictly follows the 'single responsibility' principle, and according to the responsibilities and purposes of each component, the entire project is decomposed and refined into multiple independent component modules, which reduces the coupling between codes to the greatest extent and makes it easier to focus and locate problems.
- Extracts common components into an independent project, independent compilation, and on-demand selection, greatly reducing the code quantity of the main project. Related components have also been uploaded to the Maven Central Repository, reducing the compilation time of the main project code, improving and enhancing CICD efficiency.
The original main project code structure has also been deeply adjusted, and the code package has become more reasonable, and the code logic has become clearer.
- Additional explanation:Spring Authorization ServerThis project will mainly maintain Spring Security OAuth2version in the future. The original version based on Spring Security OAuth2has been moved to the spring-security-oauth2 branch, and can be obtained from the branch or release page. In the future, it will be decided whether to continue maintaining
- version based on the ISSUE and user feedback situation.
- Based on Vue3, Vite3, Vuetify3, Pinia, etc. new version front-end has been released, and the original front-end code developed based on Vue2, Vuetify2, Typescript has been moved to the vue2+vuetify2+typescript branch.
- Since version 2.7.2.3, Dante Cloud has opened all core codes.
- Newly opened contents include:@PreAuthorizeInterface permission authentication: fully integrates URLannotation permissions with Spring Securitypermissions, through backend dynamic configuration, no need to configure
- permissions annotation and permission methods, to achieve interface authentication and dynamic modification of permissions. Adopting distributed authentication scheme, avoiding the pressure and repeated authentication problems of Gateway unified authentication.Spring Security @PreAuthorizeDynamic permission data distribution: adopting distributed service independent authentication scheme, URLpermissions annotation, permission methods, and
- permissions, through backend dynamic configuration, real-time dynamic distribution to corresponding services.OAuth2 UserDetailsUser data access strategy:FeignCore data supports direct database access and OAuth2remote call two modes. Direct database mode has better performance, Feignremote call mode has stronger extensibility. Can be dynamically modified through configuration to adopt strategy mode.
- Mobile SMS verification code registration authentication: adopting custom OAuth2authorization mode, using unified Tokeninterface, implementing mobile verification code login authentication, with the platform as a unified system, unified returning OAuth2Token, supporting service interface authentication.
- Third-party system social registration authentication: integrating JustAuthadopting custom OAuth2authorization mode, using unified Tokeninterface, implementing third-party system social login authentication based on JustAuthwith the platform as a unified system, unified returning OAuth2 Token, supports service interface authentication. All JustAuth All supported third-party systems are supported.
- WeChat mini-program registration authentication: Adopting custom OAuth2authorization mode, using unified Token interface, implementing support for WeChat mini-program login authentication and unified platform, unified return OAuth2 Token, supports service interface authentication.
- Other registration authentication methods: Adopting strategy mode for external system login authentication and user registration to support interface, adopting OAuth2 default authentication interface. Currently, non-integrated external systems, please refer to the standard, and adjust parameters as needed to support interface.
- Multi-channel SMS integration: Integrating Ali, Baidu, China Mobile, Huawei, JD, Jiguang, NetEase, Qiniu, Tencent, Yaapi, Yunpian, etc. platforms for short message sending channels. Can be dynamically selected through configuration. Supports multiple template definitions and template parameter order control.
- WeChat mini-program subscription message: Supports sending WeChat mini-program subscription messages. Provides subscription message template factory, can be written with a small amount of code to extend support for new subscription message templates.
5. Tech Stack
Enterprise-level technical middleware microservice architecture and service capability development platform.
Based on Spring Authorization Server 0.3.1, Spring Boot 2.7.3, Spring Cloud 2021.0.3, Spring Cloud Alibaba 2021.0.1.0, Nacos 2.1.1 development, highly modularized and configurable, very suitable for learning and enterprise use as a basic framework.
[1] Overall architecture

Part of the function demonstration, adding step by step
(1) Method-level dynamic permissions

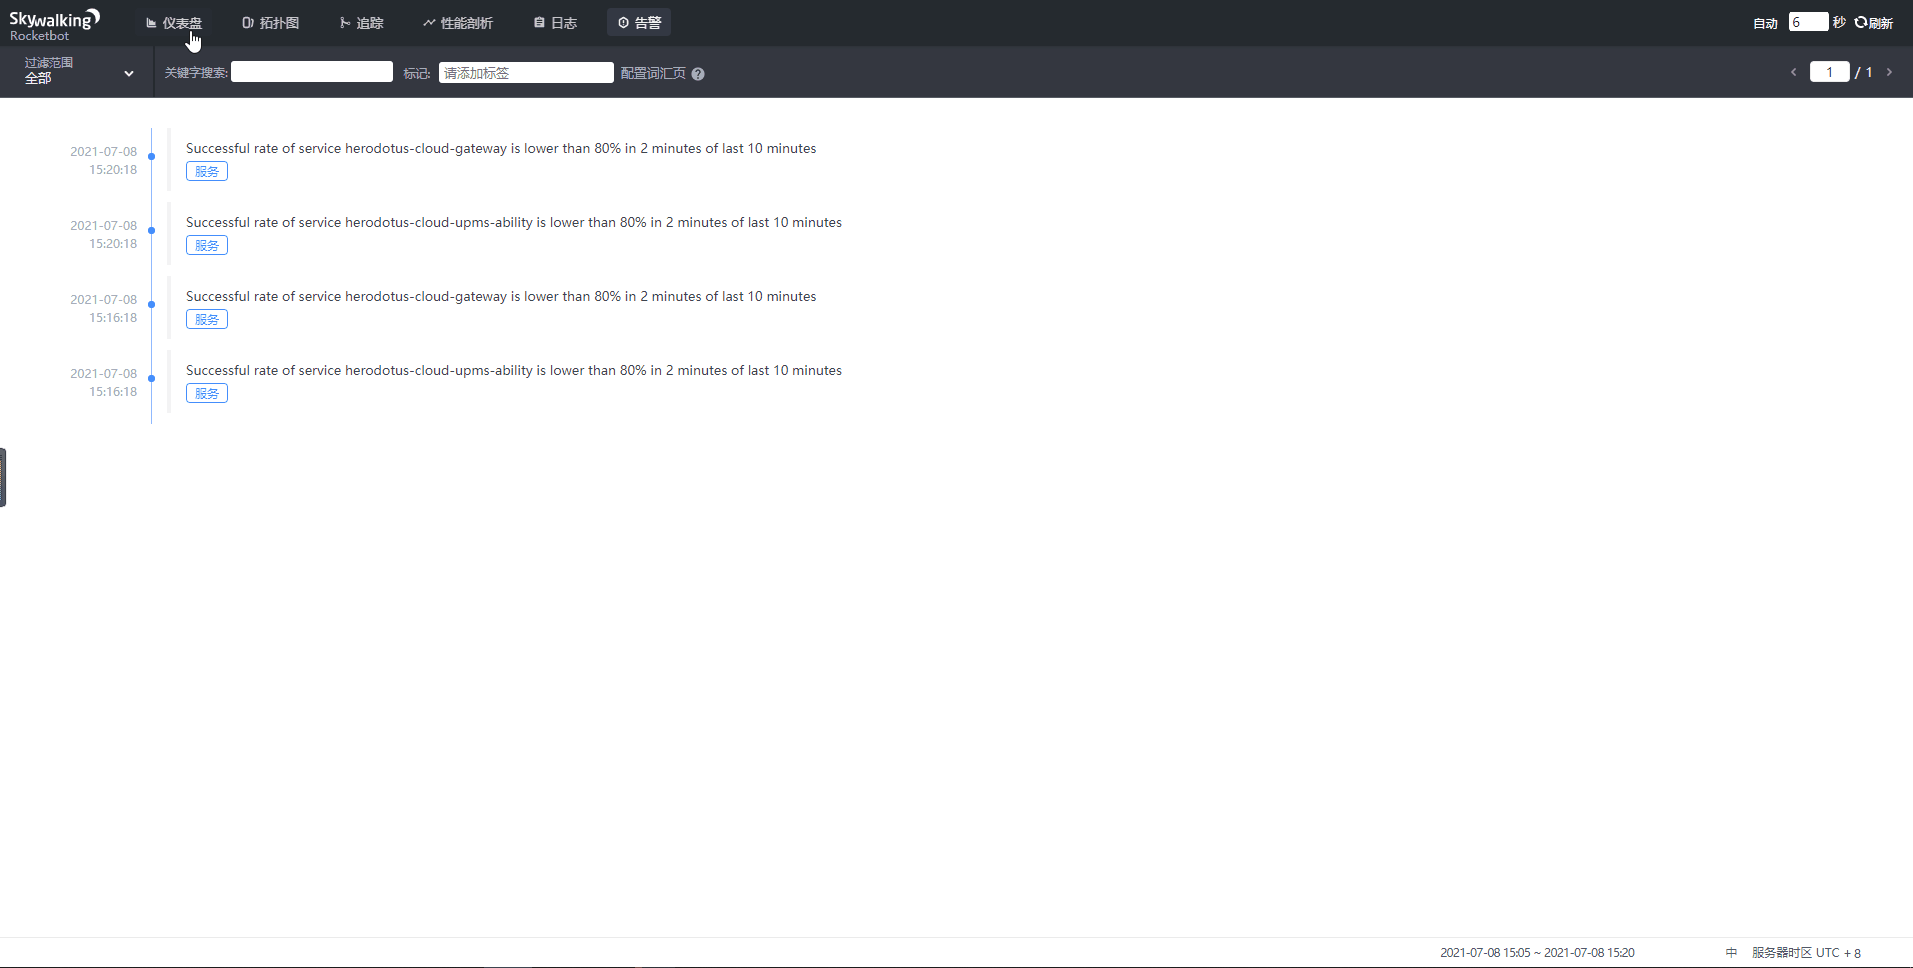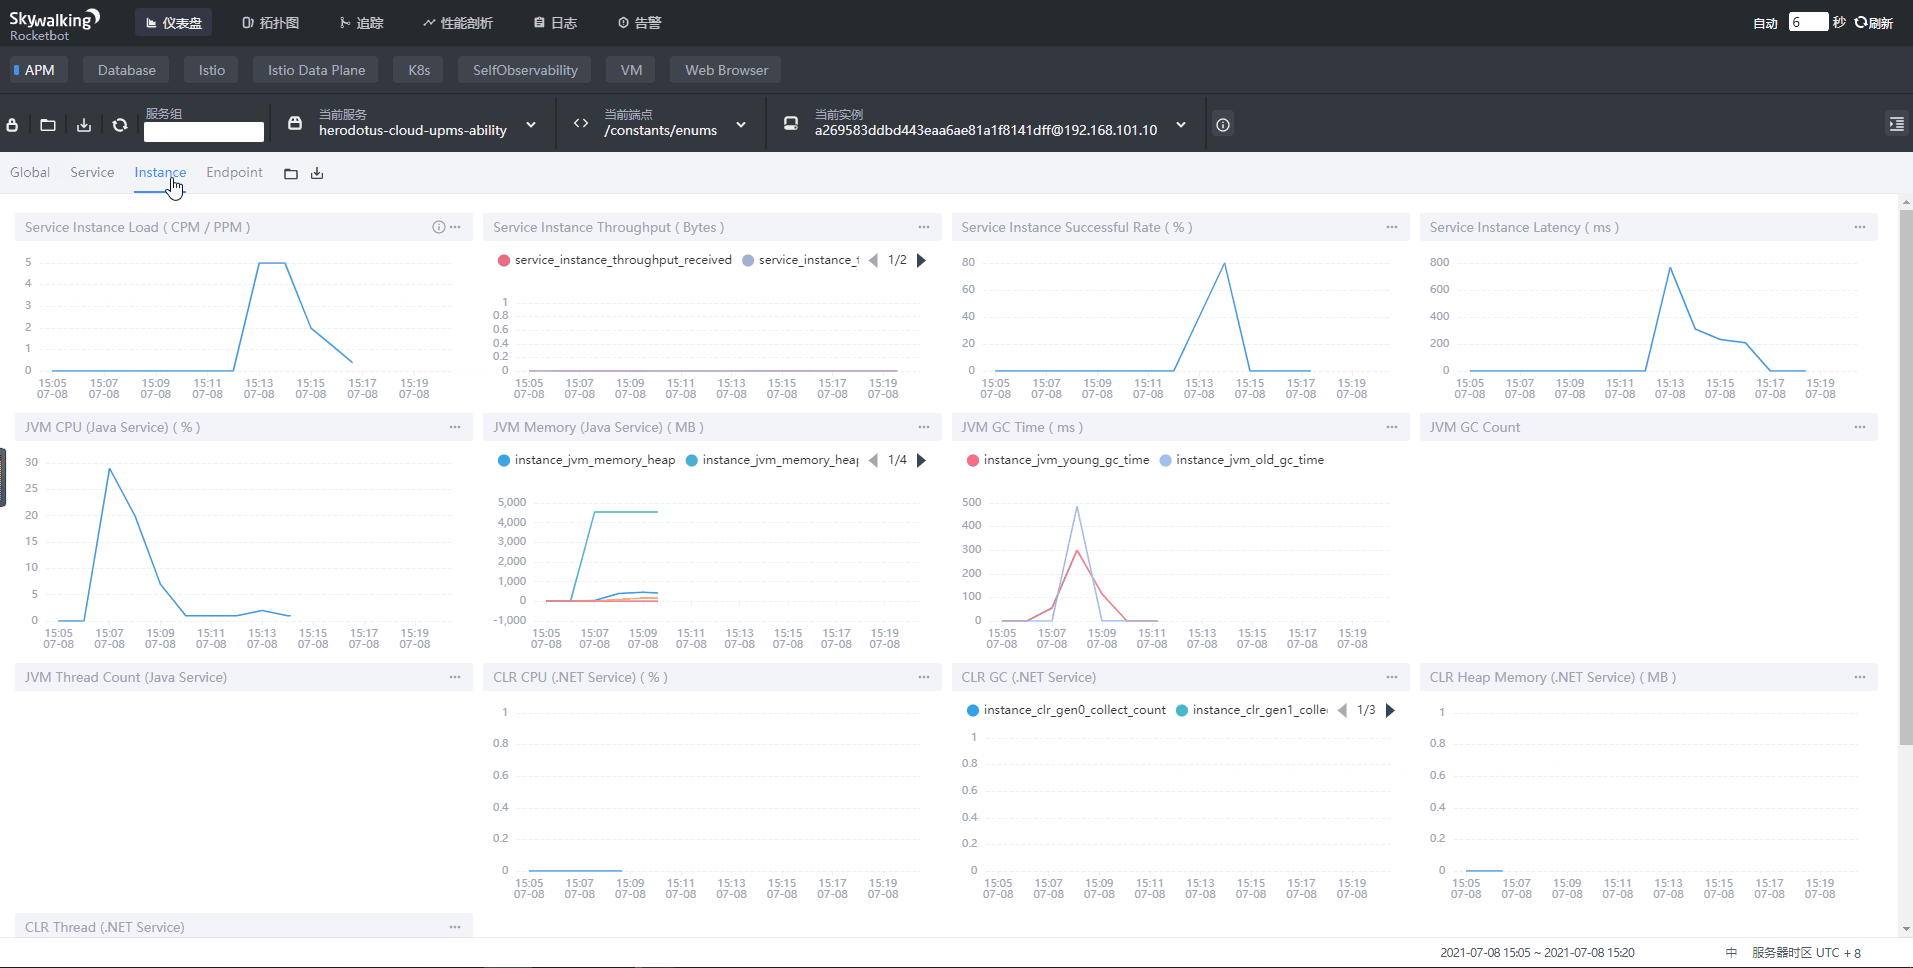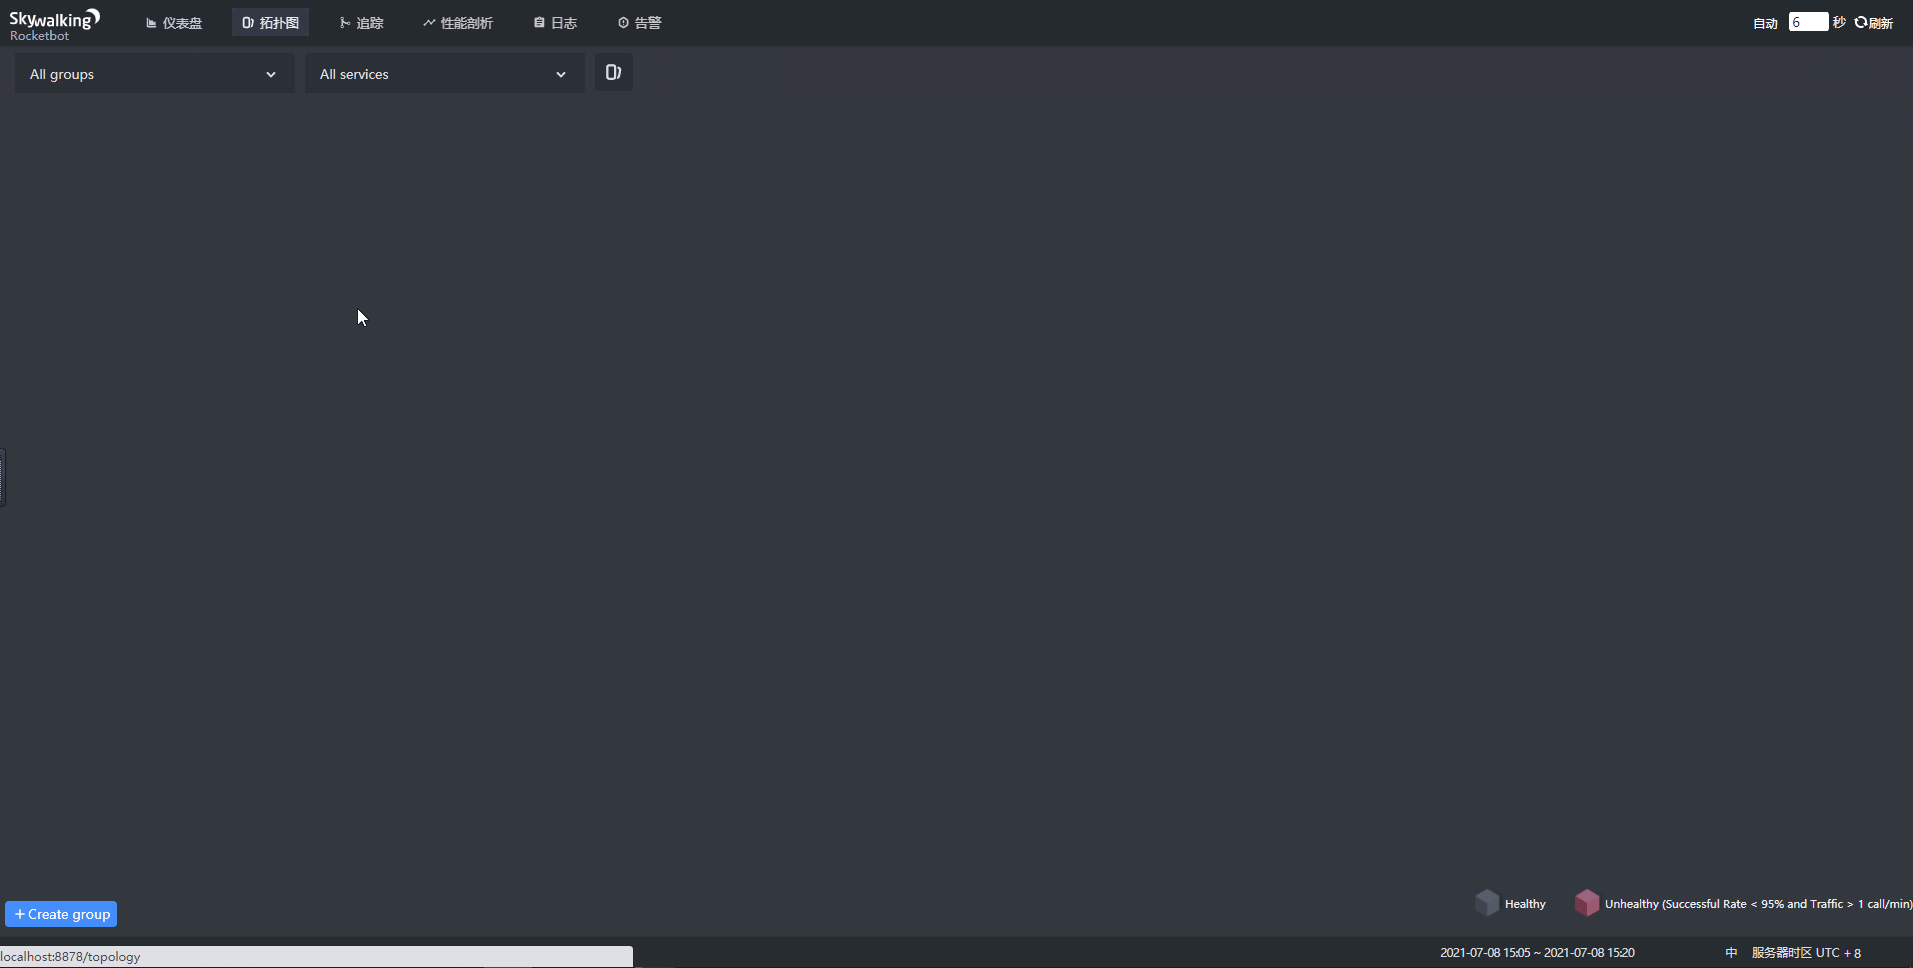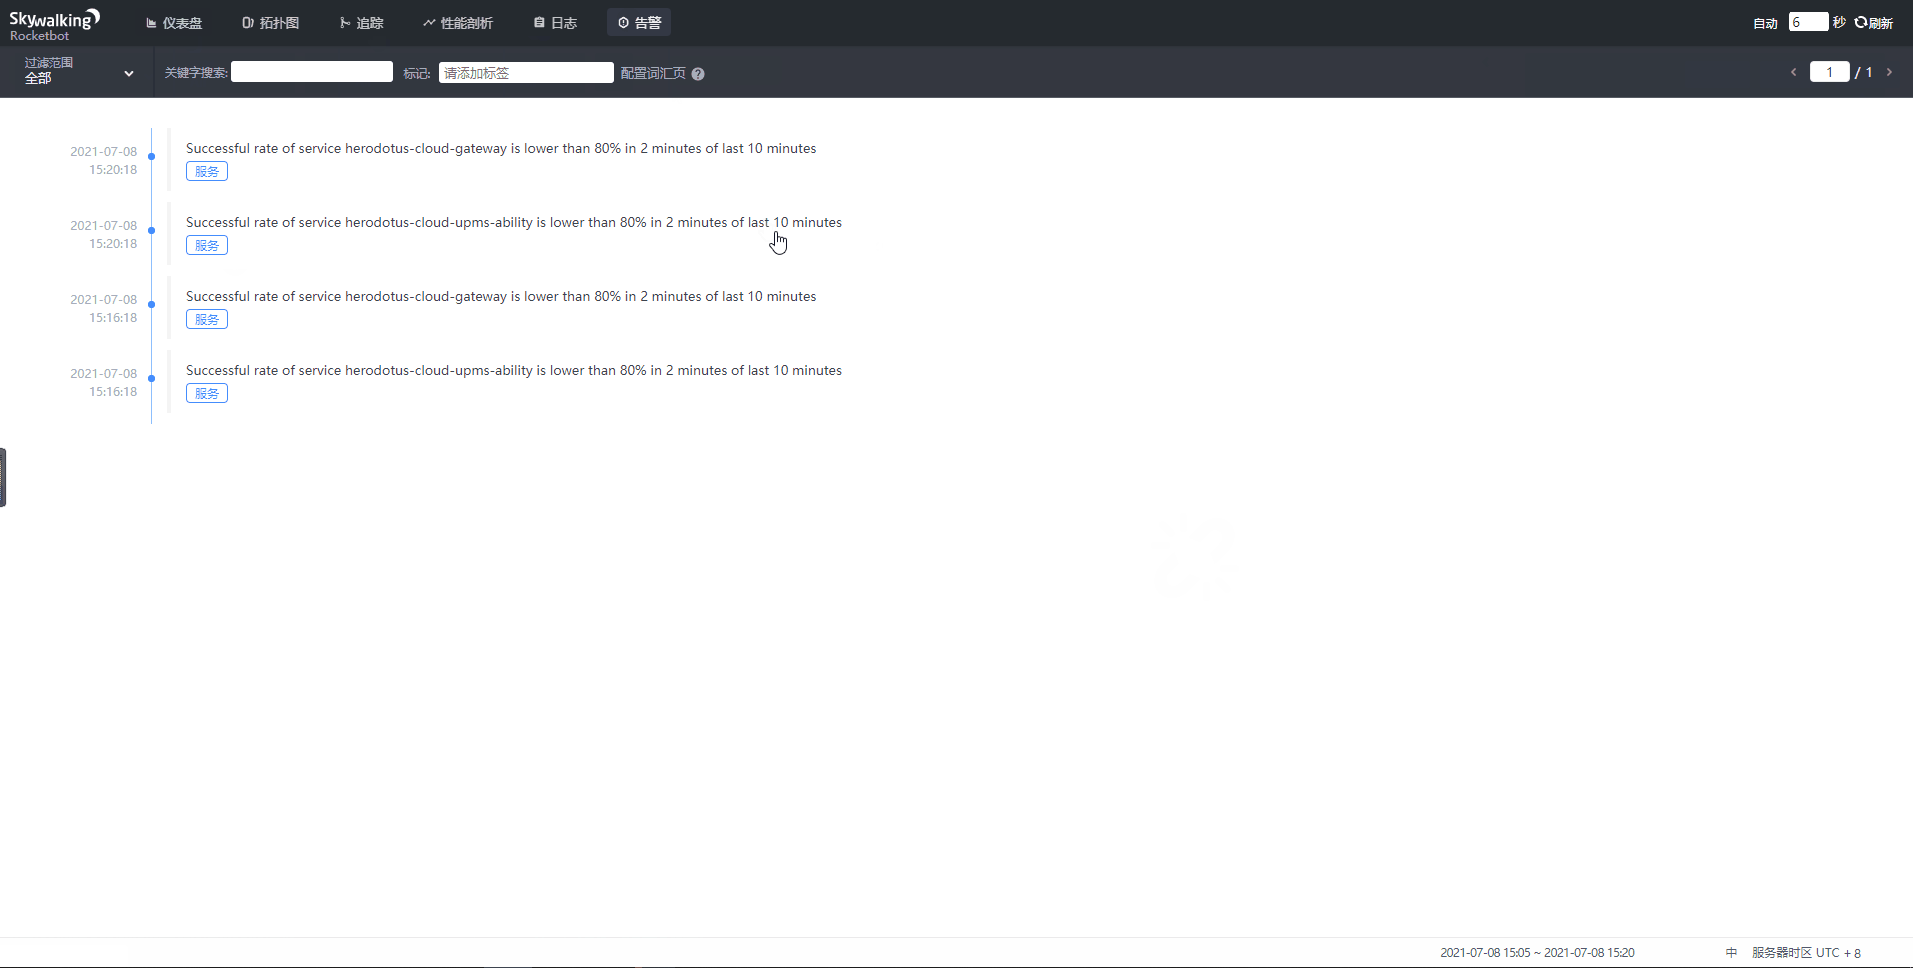
(2) Service call chain monitoring
(3) Flexible customization of verification codes
- Slide puzzle verification code

- Text point selection verification code

[2] Function introduction
See online documentation for details
[3] Technical stack and version explanation
(1) Spring full set and core technology version
Components
Version
Spring Boot
2.7.3
Spring Cloud
2021.0.3
Spring Cloud Alibaba
2021.0.1.0
Spring Authorization Server
0.3.1
Spring Boot Admin
2.7.4
Nacos
2.1.1
Sentinel
1.8.3
Seata
1.3.0
Spring full set version correspondence, see: version explanation
(2) Related technologies involved:
- Persistence layer framework: Spring Data Jpa & Mybatis Plus
- API gateway: Spring Cloud Gateway
- Service registration & discovery and configuration center: Alibaba Nacos
- Service consumption: Spring Cloud OpenFeign & RestTemplate & OkHttps
- Load balancing: Spring Cloud Loadbalancer
- Service fuse & degradation & limit: Alibaba Sentinel
- Service monitoring: Spring Boot Admin
- Message queue: Using Spring Cloud message bus Spring Cloud Bus default Kafka adaptation RabbitMQ
- Traceability: Skywalking
- Distributed transaction: Seata
- Data caching: JetCache + Redis + Caffeine, custom multi-level caching
- Database: Postgresql, MySQL, Oracle ...
- JSON serialization: Jackson & FastJson
- File service: Aliyun OSS/Minio
- Data debugging: p6spy
- Log center: ELK
- Log collection: Logstash Logback Encoder
(3) Front-end engineering technology stack
- Vue3
- Vite3
- Pinia
- Typescript
- Quasar2
- Vue-Router 4
- Vueliate
[4] Version number explanation
This system version number, divided into four segments.
- First and second segments, corresponding to Spring Boot version, changing according to adopted Spring Boot version. For example, currently adopting Spring Boot 2.4.6 version, then starting with 2.4.X.X
- Third segment, indicating system function changes
- Fourth segment, indicating system function maintenance and optimization
[5] Project structure
dante-cloud
├── configurations -- Configuration files scripts and unified Docker build context directory
├── dependencies -- Project Maven top-level dependencies, unified control versions and dependencies
├── module -- Dependency components semi-finished assembly project
├    ├── dante-module-common -- Module related module public auxiliary code components
├    ├── dante-module-security -- Security related configuration code module components
├    ├── dante-module-upms-logic -- UPMS basic management and shared code module components
├    └── dante-module-upms-rest -- UPMS basic management interface module components
├── packages -- Basic core Starter
├    ├── authorization-spring-boot-starter -- OAuth2 authentication basic Starter, mainly used for UAA authentication server and single-body Dante Cloud
├    └── service-spring-boot-starter -- Platform access application service common Starter
├── platform -- Platform core service
├    ├── dante-cloud-gateway -- Service gateway
├    ├── dante-cloud-monitor -- Spring Boot Admin monitoring service
├    ├── dante-cloud-upms -- Unified permission management system service
├    └── dante-cloud-uaa -- Account management and unified authentication module
├── services -- Platform business service
├    ├── dante-cloud-bpmn-ability -- Workflow service
├    ├── dante-cloud-bpmn-logic -- Workflow basic code package
├    ├── dante-cloud-cmdb-ability -- Simplified CMDB management service
└──  └── dante-cloud-cmdb-logic -- Simplified CMDB basic code package